How to Handle Anti-Money Laundering for German Companies
Last Updated: October 16, 2026
Who Must Comply: Obliged Entities Under the German Anti-Money Laundering Act
Anti-money laundering compliance is not optional for a large share of German companies. The Anti-Money Laundering Act (Geldwäschegesetz, or GwG) sets out who must comply, and the list is longer than most founders expect. If your business model touches any of the following, you are likely an obliged entity under the GwG:
- Credit and financial institutions
- Lawyers, notaries, and tax advisors
- Auditors and accountants
- Real estate agents and property developers
- Insurance brokers
- Trust and company service providers
- Traders in high-value goods, including certain e-commerce sellers
- Anyone handling virtual assets or cryptocurrency services
The GwG aims to stop money laundering and terrorist financing, and it applies to you based on what you do, not where your owners live.
The obligations are not just paperwork. They include risk analysis, internal safeguards, customer due diligence, and reporting duties. Germany's regulator for these duties is BaFin, and the central reporting body is the Financial Intelligence Unit (FIU).
AML Risk Assessment for Companies: A Step-by-Step Approach
An AML risk assessment for companies is the written analysis of how your business could be misused for money laundering or terrorist financing.
The GwG follows a risk-based approach. Your controls must match your actual risk, not a generic template. A three-person e-commerce seller and a real estate agency with cross-border clients should not have the same programme.
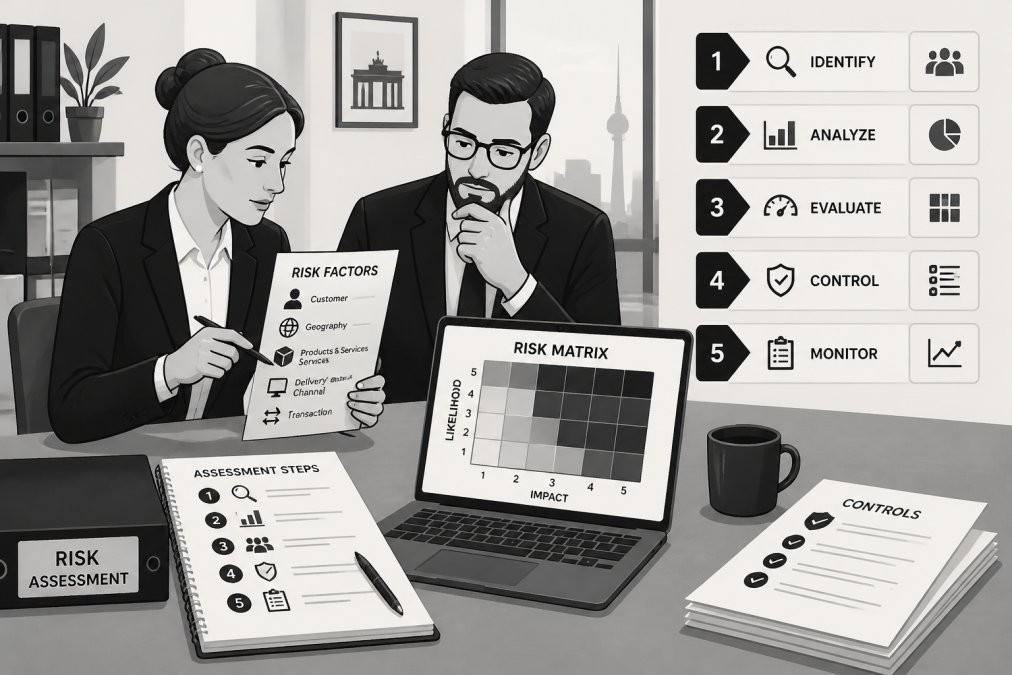
Step 1, Map your business model
Write down, in plain language:
- Products and services you actually sell
- Customer types (private individuals, companies, trusts, nominees)
- Payment methods (bank transfer, card, cash, virtual assets)
- Countries you serve and countries your customers come from
- Delivery channels (in person, online, via intermediaries)
This map is the scope of your assessment. Anything not on the map is not assessed.
Step 2, Identify risk factors
Work through the standard categories. Most practitioners use four:
- Customer risk, PEPs, high-risk jurisdictions, opaque ownership, cash-intensive businesses
- Product/service risk, anonymity, cash, virtual assets, high-value goods
- Geographic risk, countries on the EU's high-risk third-country list, or on the FATF's call-for-action list
- Delivery channel risk, non-face-to-face onboarding, agents, introducers
Step 3, Score each risk
A simple, defensible model is likelihood × impact on a 1-3 scale:
| Likelihood | Impact | Score | Rating |
|---|---|---|---|
| 1 (unlikely) | 1 (minor) | 1-2 | Low |
| 2 (possible) | 2 (moderate) | 3-4 | Medium |
| 3 (likely) | 3 (severe) | 6-9 | High |
You do not need a sophisticated model. You need one you can explain and reproduce.
Step 4, Set controls per risk
Every medium and high rating must map to a named control. Examples:
- High-risk jurisdiction → enhanced due diligence and senior sign-off
- Non-face-to-face onboarding → certified identity verification method
- Complex ownership → documented look-through to the beneficial owner
- Cash-intensive customer → tighter transaction monitoring thresholds
Step 5, Document, date, and review
Your written risk analysis should record:
- The date it was prepared and the person who approved it
- The methodology and scoring scale used
- Each identified risk, its rating, and the control assigned
- The review date and the trigger for an out-of-cycle review
A common cadence is an annual review, plus an ad-hoc review whenever your business model changes, new product, new country, new payment channel, or a change in ownership.
Treat the risk assessment as a living document, not a filing. Date it, version it, and keep the previous versions, auditors often ask what changed and why.
Customer Due Diligence in Germany: Identification, Beneficial Ownership, and PEP Checks
Customer due diligence in Germany means identifying your customer, verifying their identity, and understanding who really owns or controls them before you start the business relationship.
This is the core of the know your customer principle. For each customer, you should:
- Collect name, address, and date of birth for individuals
- Verify identity using a reliable document or an equivalent method
- Identify the beneficial owner, meaning the natural person who ultimately owns or controls the customer
- Check whether the customer is a politically exposed person (PEP)
- Run sanctions screening against applicable lists
The GwG requires you to identify the beneficial owner and take reasonable steps to verify that identity.
You must also keep records of what you checked and when. This creates the audit trail that supervisors and auditors expect.
Enhanced Due Diligence and Ongoing Monitoring for High-Risk Customers
Enhanced due diligence applies when a customer or transaction carries higher risk, and it means you check more, not less. Ongoing monitoring means you keep watching the relationship after onboarding.
Higher-risk situations often include:
- Customers from or connected to high-risk countries
- PEPs and their close associates
- Complex or opaque ownership structures
- Large or unusual cash transactions
- Cryptocurrency and other virtual asset flows
For these customers, you gather more evidence, get senior sign-off, and review the relationship more often. You watch transactions for patterns that do not fit the customer's profile. (Source: risk-based approach)
A practical setup tracks three things:
| Monitoring Layer | What You Watch | Typical Trigger |
|---|---|---|
| Customer profile | Changes in ownership or activity | New beneficial owner |
| Transaction pattern | Amounts, frequency, geography | Unusual cash flow |
| Sanctions and PEP lists | Name and entity matches | List update |
If a transaction looks suspicious, you do not stop at monitoring. You move to reporting.
AML Compliance Checklist: Internal Safeguards, Staffing, and Records
An AML compliance checklist keeps your internal safeguards, staffing, and recordkeeping in one place. The GwG expects internal safeguards proportionate to your risk profile, principles, procedures, and controls that are written down, assigned to someone, and reviewable.
The AML officer (Geldwäschebeauftragter)
Where the GwG requires one, the AML officer is the named person responsible for the day-to-day running of your programme. In practice that means:
- Maintaining and updating the risk analysis
- Owning the internal policies and procedures
- Deciding on escalated customer cases and enhanced due diligence
- Filing suspicious activity reports with the FIU
- Keeping training records and the audit trail
- Acting as the contact point for BaFin and the FIU
The officer needs authority, not a large team. For many SMEs, one trained internal officer supported by outside advice is enough. What matters is that the role is documented, resourced, and not merely a title on paper.
Internal safeguards checklist
Use this as a starting point and adapt it to your risk profile:
- Written risk analysis, dated, versioned, and reviewed at least annually
- Internal policies and business procedures in plain language
- A named AML officer where required, with a written role description
- Employee training at onboarding and repeated at intervals
- Identity verification steps for every customer before the relationship starts
- Beneficial ownership records, including the look-through to natural persons
- Sanctions and PEP screening process, with a defined re-screening trigger
- Transaction monitoring rules tied to the risk analysis
- A clear internal path for escalating and filing a suspicious activity report
- Recordkeeping with retention periods in line with the GwG
Recordkeeping and retention
The GwG sets retention periods for AML records, and the practical rule is simple: if you cannot produce the evidence, the control did not happen. Keep:
- The risk analysis and each version of it
- Customer identification and verification records
- Beneficial ownership documentation
- Screening results and the date they were run
- Training logs with names and dates
- Internal escalation notes and filed reports
Store records so they can be retrieved on request, and align the retention period with the GwG's requirements for the relevant record type. When in doubt, check the current rules on the BaFin and FIU websites rather than relying on a template.
Staffing for SMEs
Staffing is where small firms hesitate. You do not need a compliance department. You need:
- One responsible person who knows the rules and has the authority to act
- A deputy, so the role survives holidays and turnover
- A documented handover when the role changes hands
For many SMEs, a trained internal officer supported by outside advice is the proportionate answer.
AML Red Flags for Businesses: When and How to Report to the FIU
Typical red flags include:
- A customer who is reluctant to provide identity documents
- Ownership structures that change without a clear reason
- Payments from unrelated third parties
- Transactions that do not match the customer's known business
- Sudden large cash flows
- Requests to split payments to stay below reporting thresholds
When you spot a red flag, you assess it. If suspicion remains, you file a suspicious activity report with the Financial Intelligence Unit.
The reporting threshold for cash is a figure you should confirm with the official sources, because it can change.
Failing to report can lead to administrative fines and, in serious cases, criminal liability for the individuals involved. The duty sits with the company and its officers.
Proportionality and Implementation for SMEs: Costs, Staffing, and Technology
Proportionality means your AML programme should match your size and risk, and for SMEs that is good news.
A workable SME approach looks like this:
- One trained AML officer, part-time if needed
- Simple written procedures in plain language
- Off-the-shelf screening tools for sanctions and PEP checks
- Basic monitoring rules tied to your risk analysis
- Annual review and update
Technology helps here. Screening software and automated identity checks reduce manual work and create cleaner records.
Costs vary widely by business model, transaction volume, and how much you automate.
Implementation for SMEs usually takes weeks, not months, if you start with the risk analysis and build outward.
Conclusion: Building a Proportionate, Documented AML Programme
The hardest part of anti-money laundering compliance is not understanding the rules. It is proving you followed them. A proportionate, documented programme turns a legal duty into a routine you can run and defend.
If you are setting up a German entity and want a clean, compliant structure from the start, German-Nominee.de has helped international founders since 1984. Our licensed German nominee shareholder and trustee structure is built for full compliance with German notary requirements, with no travel needed.
Frequently Asked Questions
Is Germany a high-risk country for anti-money laundering?
Germany is not classified as a high-risk third country by the FATF, but it faces significant money laundering risks due to its large financial sector and cash-intensive economy. The German Anti-Money Laundering Act (GwG) implements EU directives and sets strict obligations for obliged entities. Companies must conduct risk assessments, apply customer due diligence, and report suspicious activity to the Financial Intelligence Unit (FIU).
Which companies in Germany must comply with anti-money laundering requirements?
Obliged entities under the GwG include credit institutions, financial services providers, insurance companies, lawyers, notaries, tax advisors, auditors, real estate agents, and dealers in goods if payments exceed certain thresholds. Trust and company service providers are also covered. If your business falls into one of these categories, you must implement internal safeguards, conduct customer due diligence, and appoint an AML officer.
What are common anti-money laundering red flags for businesses?
Common red flags include unusual cash flows, complex ownership structures without clear rationale, customers reluctant to provide identification documents, transactions just below reporting thresholds, and business relationships with high-risk jurisdictions. Politically exposed persons (PEPs) and customers in sanctioned sectors also warrant enhanced scrutiny. Documenting and escalating these red flags promptly is essential to meet reporting obligations.
How should a company conduct an AML risk assessment?
Start by identifying your business model, customer base, products, and geographic exposure. Assess inherent risks for money laundering and terrorist financing, then evaluate the effectiveness of your internal controls. Document the methodology, assign risk ratings, and update the assessment regularly. The risk-based approach should be proportionate to the size and nature of your business, and the results must inform your due diligence and monitoring procedures.